Network Monitoring · Wireshark 4.x
Wireshark Network Protocol Analyzer
Deep packet capture and protocol analysis for IPTV, OTT and broadcast network troubleshooting.
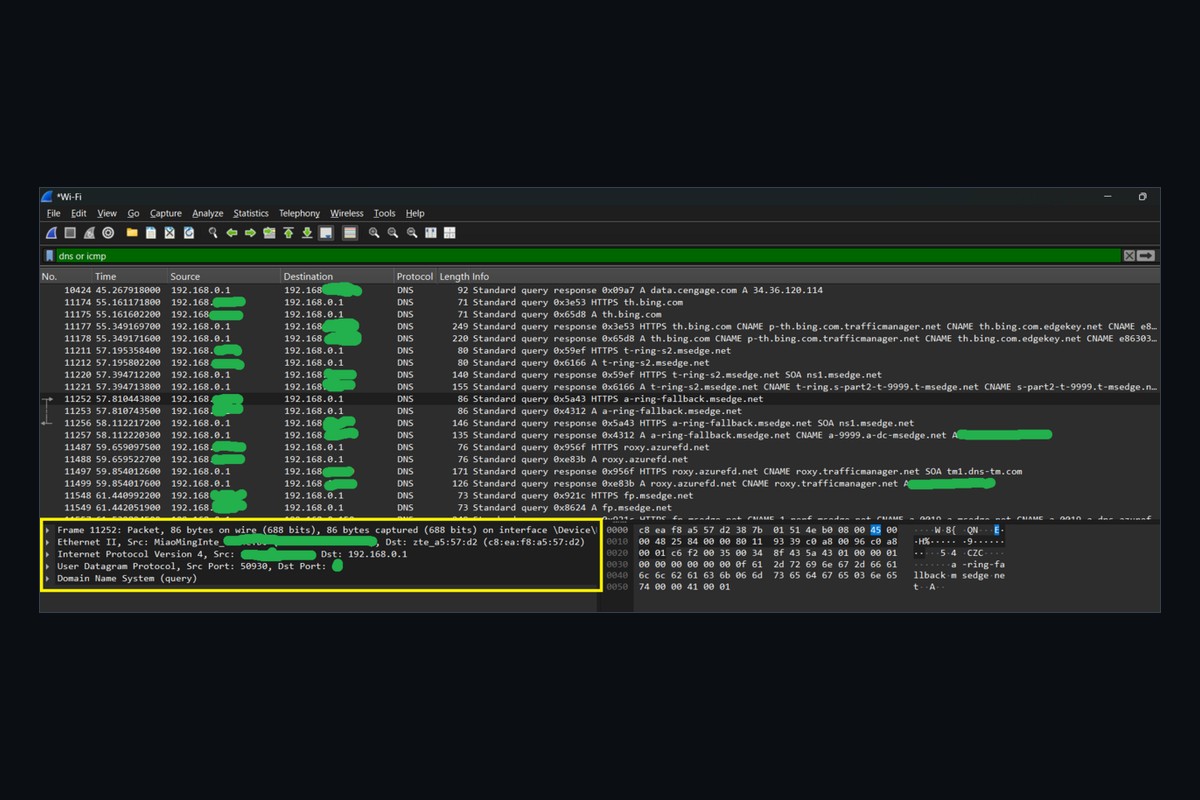
Wireshark captures and decodes traffic on headend, contribution and return-feed links, with protocol dissectors for RTP, MPEG-TS, SRT, HTTP/HLS, DASH, SMPTE 2022 and more. Engineers use it to prove packet loss, jitter, retransmissions, IGMP/PIM issues and encapsulation faults, while tshark and dumpcap support remote captures and automated analysis.
Technical specifications
- Product type
- Open-source network protocol analyzer
- Capture
- Live interfaces, pcap/pcapng files, remote capture and ring buffers
- Protocols
- 3,000+ dissectors including Ethernet, IP, TCP/UDP, RTP, MPEG-TS, SRT, HTTP/HLS/DASH, IGMP, PIM and SMPTE 2022
- Analysis
- Display filters, colouring rules, conversations, IO graphs, expert information and stream reassembly
- Decryption
- TLS key-log, IPsec and Kerberos decryption support
- CLI tools
- tshark, dumpcap, editcap and capinfos
- Extensibility
- Lua plugins and custom dissectors
- Platforms
- Windows, macOS and Linux
- Use cases
- Packet loss, jitter, multicast, return-feed and encapsulation diagnostics
Specifications are indicative and confirmed in the written quotation. Availability varies by model and region; contact us for current lead times.
Integration
Need this specified into a full headend?
Send us the channel list and service definition. We will return a signal chain design, BOM and installation plan.